
 Login
How to Set Up WestFax Single Sign-On with Okta
Create a SAML 2.0 app integration in Okta so your team launches WestFax straight from the Okta dashboard with credentials they already have.
WestFax supports SAML 2.0 single sign-on with Okta, so your team reaches the WestFax fax console through the Okta dashboard with credentials they already have — no separate WestFax password to issue or reset. Setup is a three-step round trip: turn SSO on with your WestFax account manager and copy three endpoints off the SSO tab, create a SAML 2.0 app integration in Okta and copy two values plus a certificate back, then paste those into the WestFax admin panel and save. From then on, access is governed by Okta assignment rules.
What you’ll need
- An Okta organization account with at least one user, and admin access to your Okta dashboard
- A WestFax Enterprise account with SSO enabled — see step 1 if it isn’t on yet
- The WestFax integration listing at Okta.com, if you’d rather start from the catalog entry
What you get once it’s running: control from Okta over who can reach the WestFax platform, automatic sign-in for your users, and one central place to manage the accounts.
Step 1: Turn on SSO and copy your WestFax endpoints
SSO is not on by default. Before any of the identity-provider work below will do anything, your WestFax account has to be provisioned for it — contact your account manager and ask them to activate SSO. There may be a setup fee, and they will walk you through provisioning.
Once SSO is active on the account, sign in to the WestFax admin tool and open the SSO tab. You should see a screen like this:
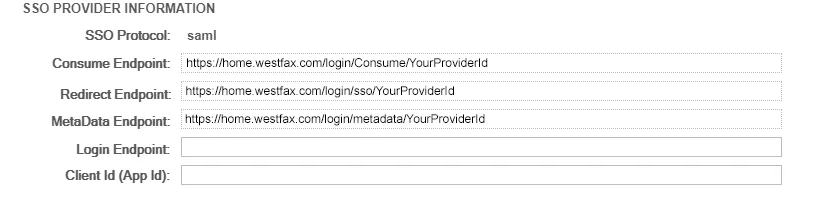
The SSO tab shows three values generated for your account. Copy all three somewhere safe — every one of them gets pasted into your identity provider in the next step. YourProviderId is unique to your WestFax account; the tab shows the real value.
- Consume Endpoint —
https://home.westfax.com/login/Consume/YourProviderId. This is the SAML assertion consumer service (ACS) URL, where your identity provider posts the signed assertion. - Redirect Endpoint —
https://home.westfax.com/login/sso/YourProviderId. This is the link your users click to sign in, and the start URL for service-provider-initiated login. - Metadata Endpoint —
https://home.westfax.com/login/metadata/YourProviderId. This is the SAML entity ID that identifies WestFax as the service provider.
Copy these straight off the SSO tab rather than typing them by hand. A single wrong character in the Consume Endpoint is the most common reason a first SSO attempt fails.
Step 2: Create the WestFax app integration in Okta
Sign in to your Okta admin dashboard at login.okta.com and build the SAML app that represents WestFax.
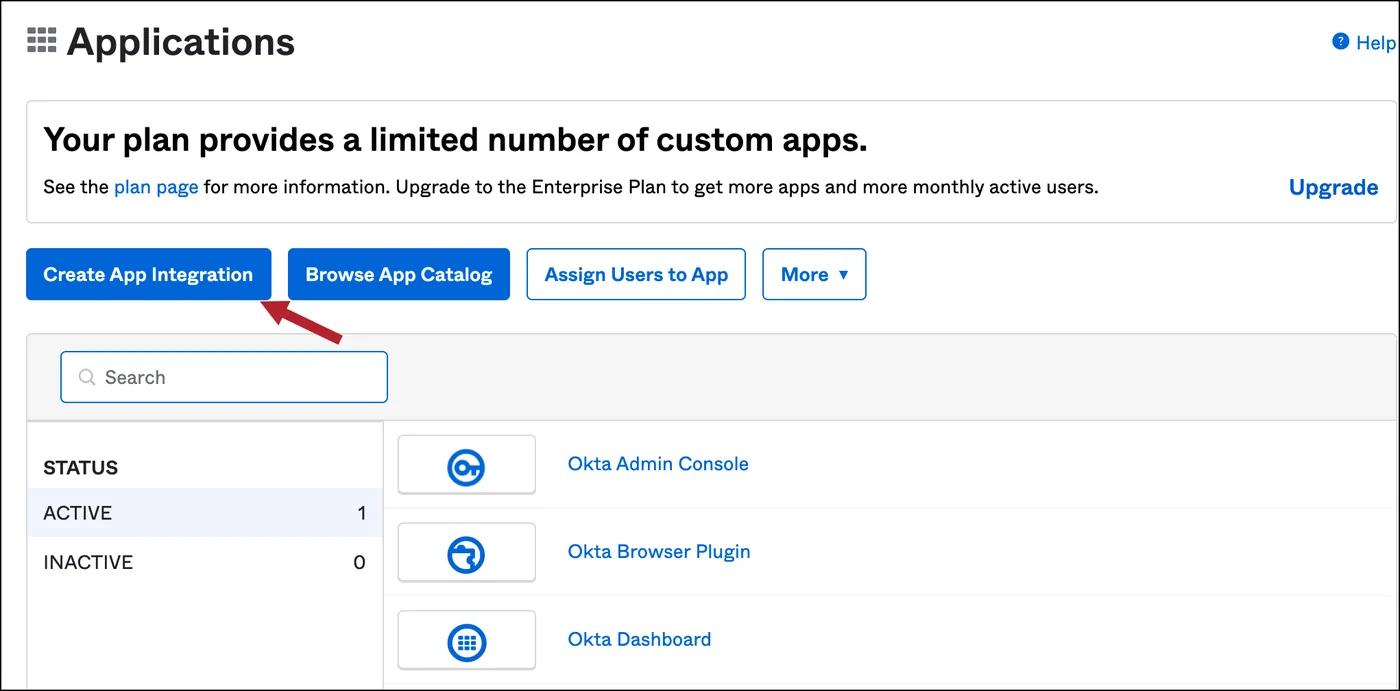
- Go to Applications → Applications.
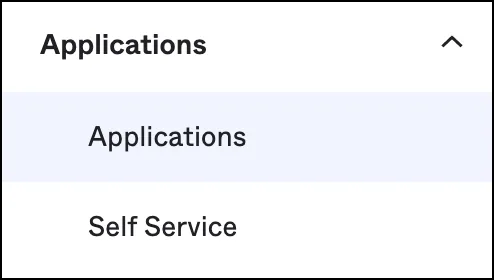
- Click Create App Integration.
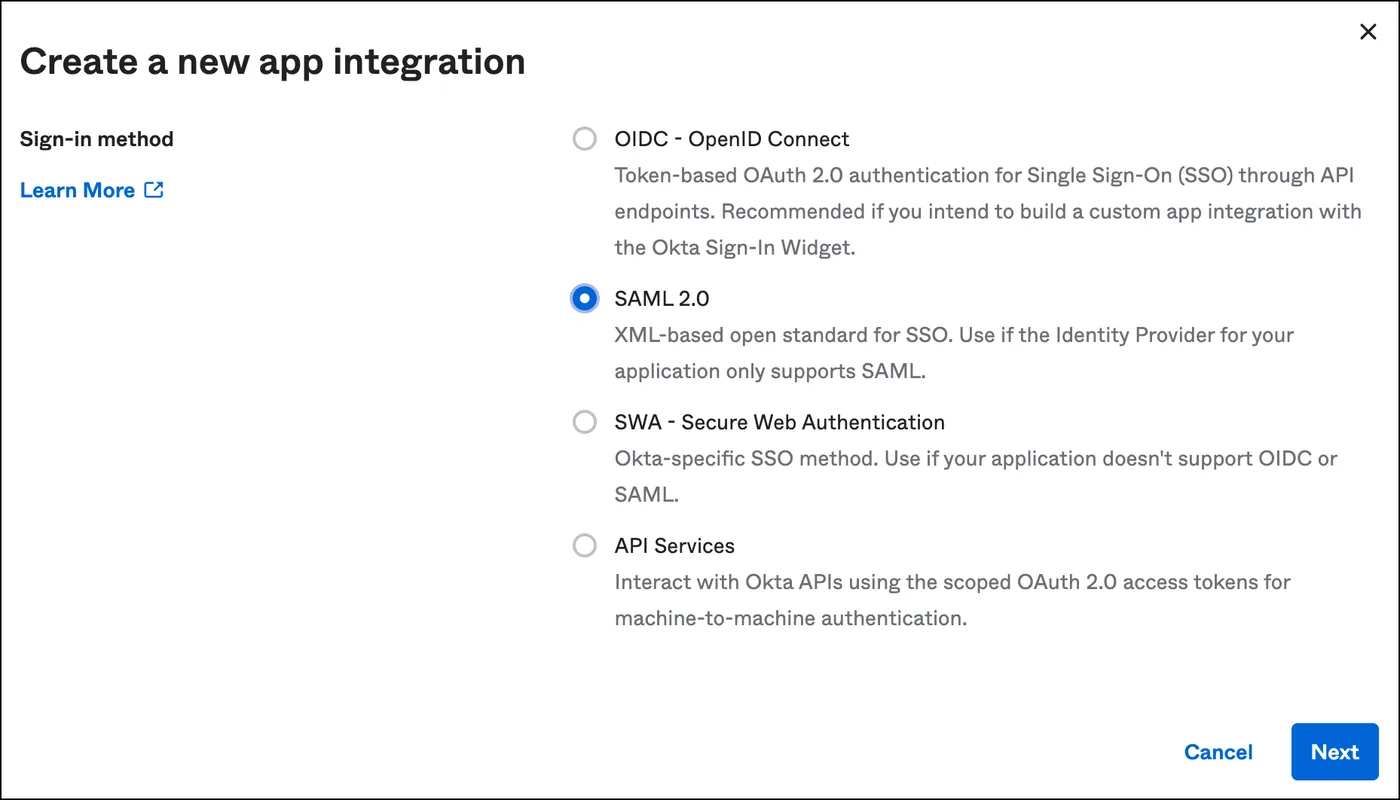
- Choose SAML 2.0 and click Next.
- Set the app name and logo. Enter
WestFaxfor the name. If you want the app tile to look right on the Okta dashboard, use the WestFax logo. Click Next.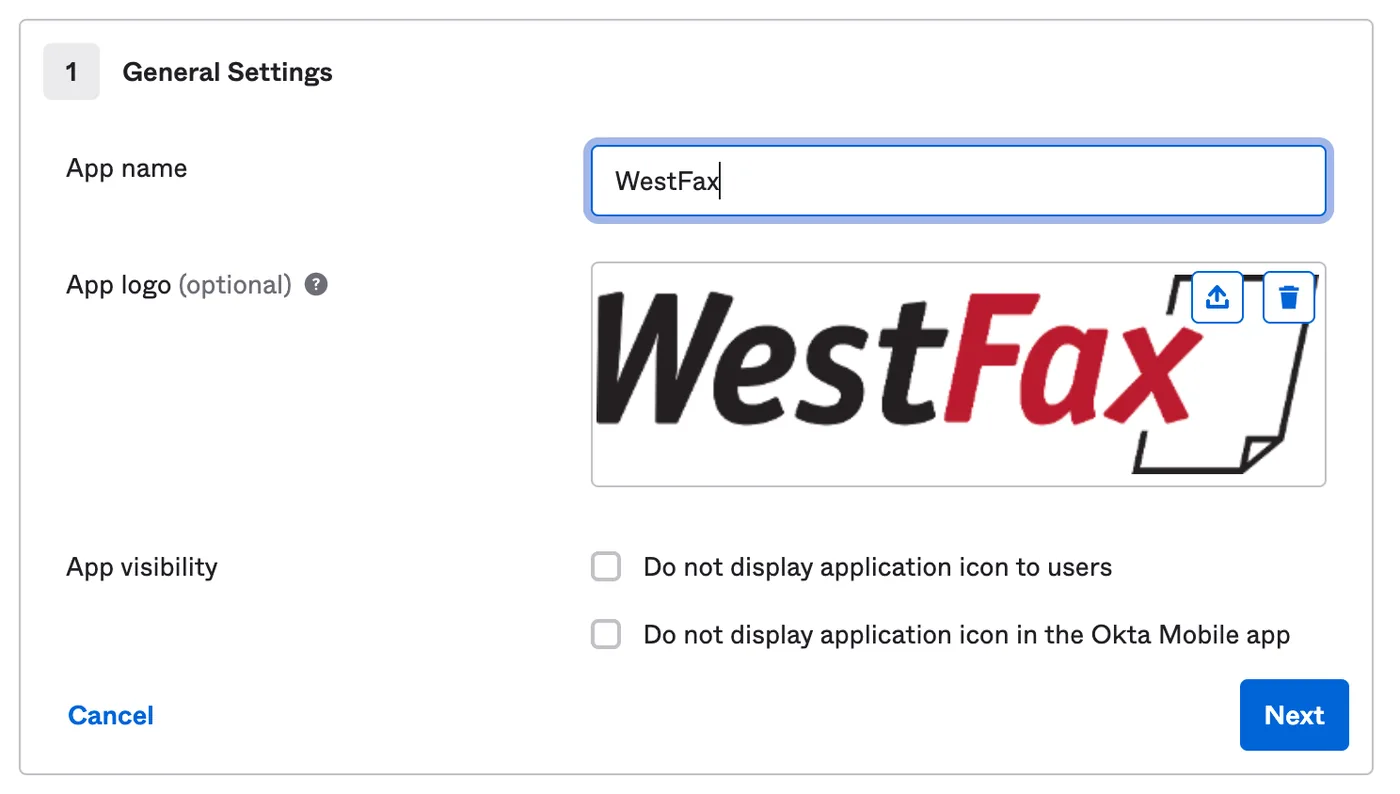
- Enter the WestFax values on the SAML Settings page. This is where the endpoints from step 1 go.
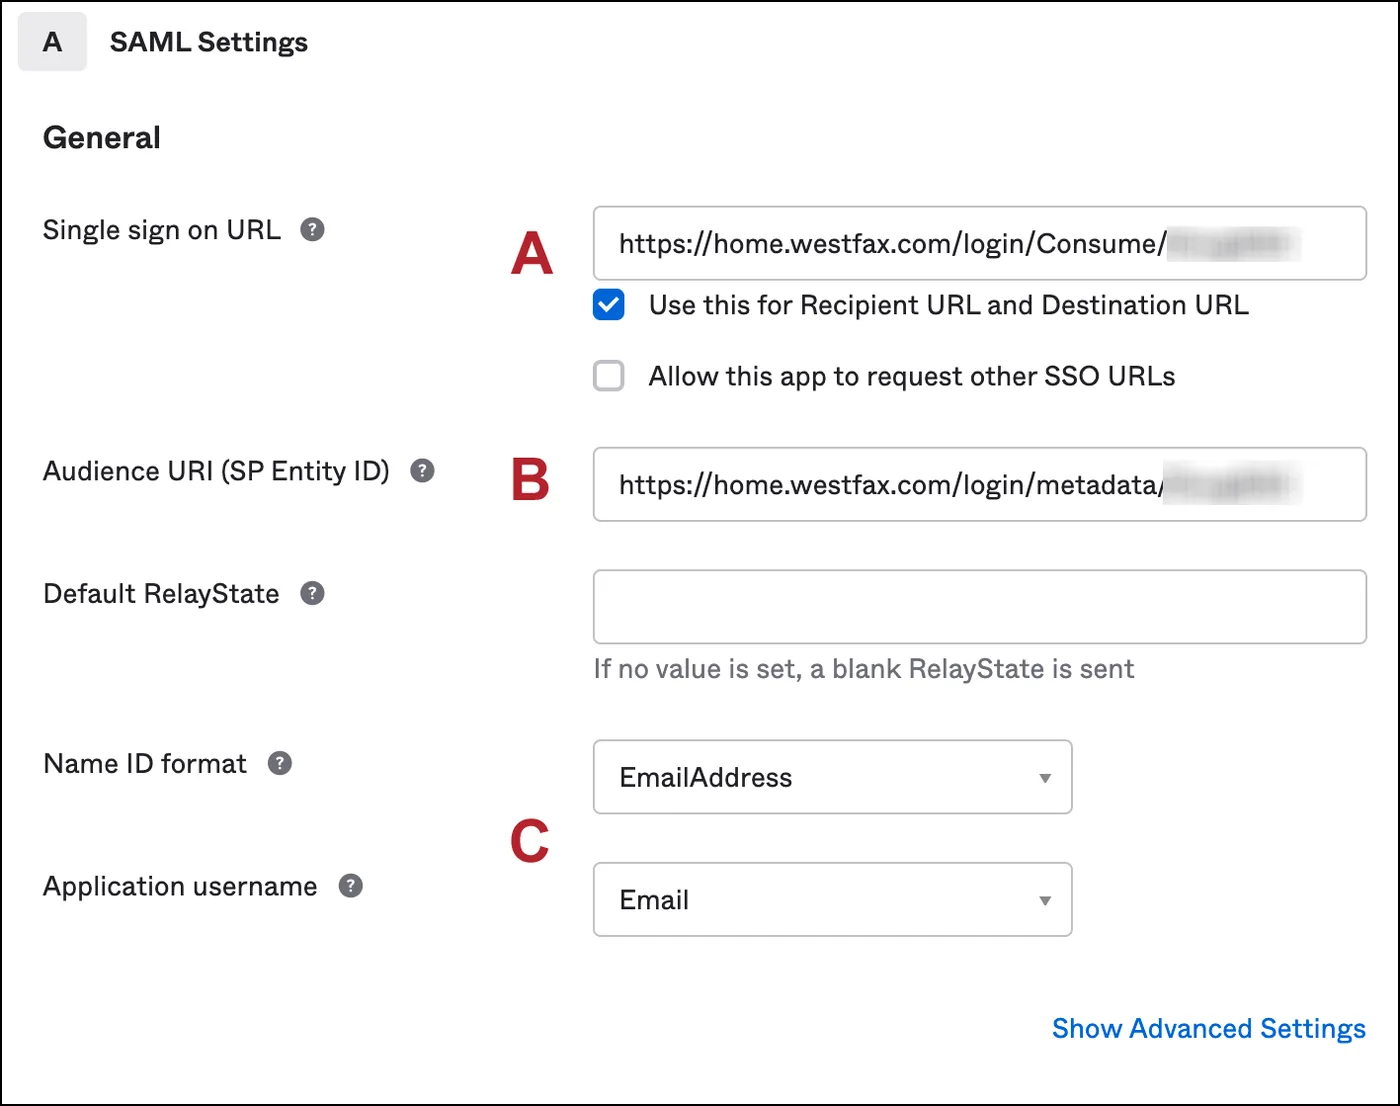
- A — Single sign-on URL:
https://home.westfax.com/login/Consume/YourProviderId - B — Audience URI (SP Entity ID):
https://home.westfax.com/login/metadata/YourProviderId - C — Name ID format / Application username:
EmailAddress/Email. Other fields can be used instead — ask us if your directory keys on something else.
Download your x.509 certificate to a secure location while you’re here. You’ll upload it to WestFax in step 3.
- A — Single sign-on URL:
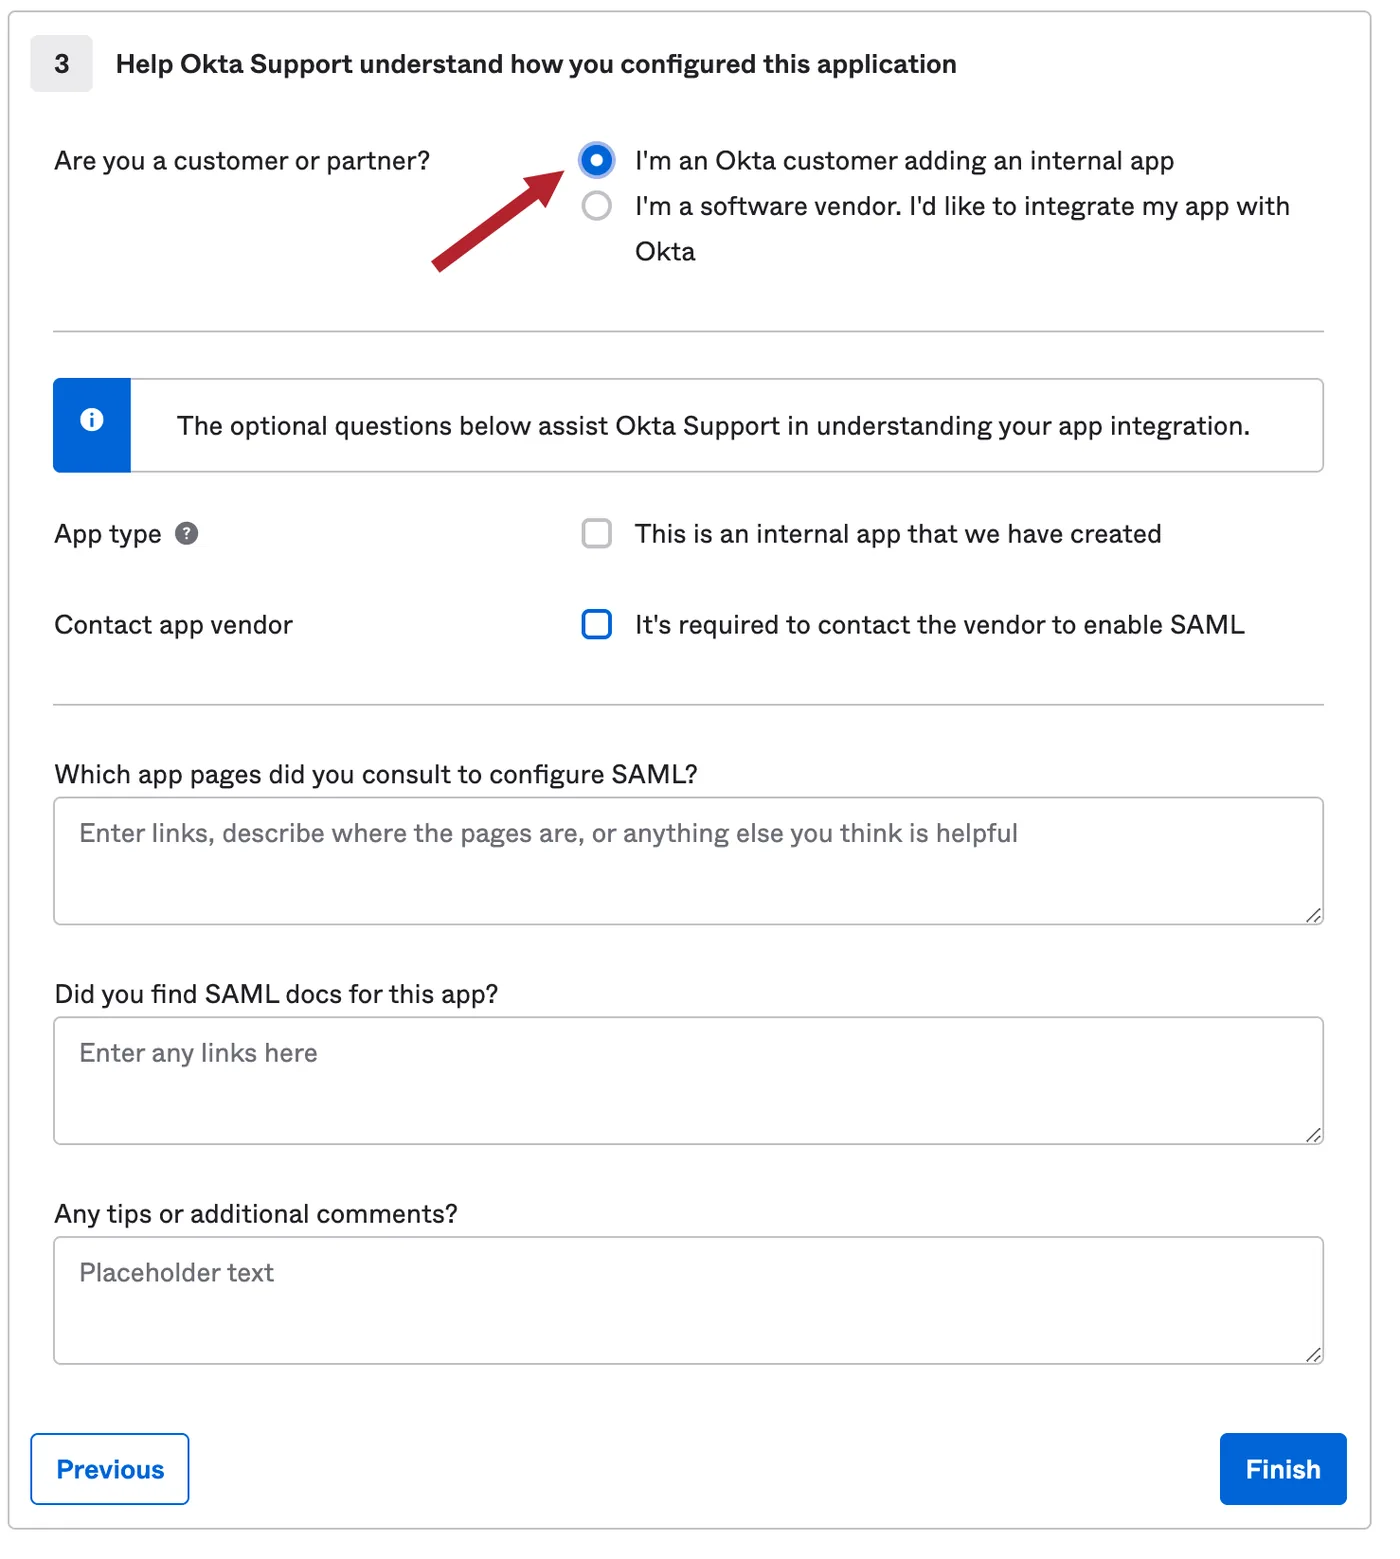
- Finish the wizard. On the feedback page, select I’m an Okta customer adding an internal app and click Finish.
- Click View Setup Instructions in the yellow box on the Sign On tab.
- Copy the first two values. Take the complete
Identity Provider Single Sign-On URL. For theIdentity Provider Issuer, copy only the unique code that followshttp://www.okta.com/— not the whole string.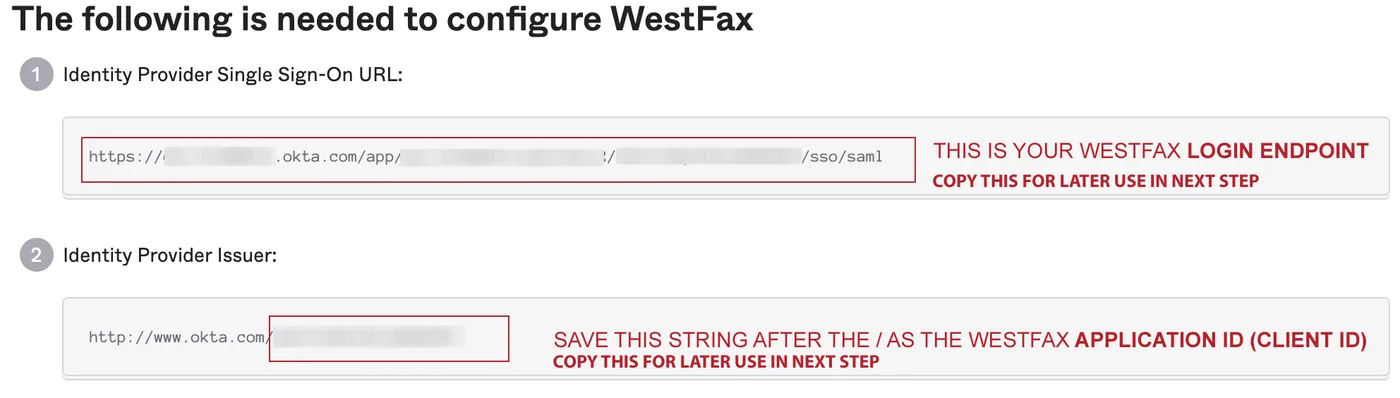

Before you test: assign the app. Open the Assignments tab and add the people or groups who should reach WestFax — an unassigned user gets an error rather than a login screen.
Step 3: Finish the setup in the WestFax admin panel
Go back to the WestFax admin panel and open the SSO section again. This is where the two values and the certificate from Okta get entered.
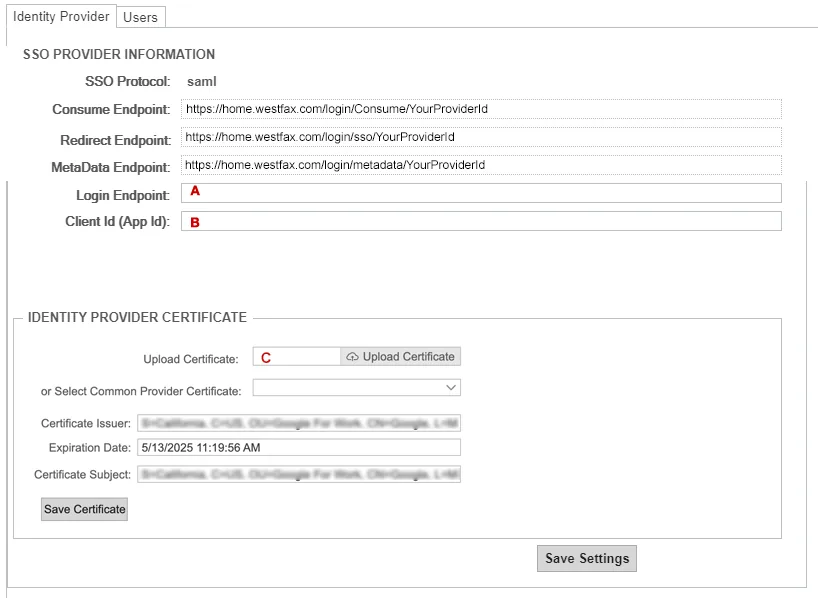
A — Login Endpoint— theIdentity Provider Single Sign-On URLfrom Okta.B — Client Id (App Id)— the unique code from theIdentity Provider Issuer, without thehttp://www.okta.com/prefix.C — Certificate x.509— the certificate file you downloaded from Okta. Click upload and select it.
Click Save Settings. That completes the configuration.
Sign in with SSO
Your team signs in through the Redirect Endpoint from step 1 — https://home.westfax.com/login/sso/YourProviderId — rather than the standard WestFax login page. Copy the exact link off the SSO tab and distribute it, or let users launch WestFax from the tile on their Okta dashboard.
Troubleshooting
- Users can’t see or launch the WestFax tile. They aren’t assigned. Add the user or their group on the app’s Assignments tab.
- Sign-in fails right after the Okta prompt. Check the single sign-on URL and audience URI against the SSO tab character for character, including
YourProviderId. - WestFax rejects an authenticated user. The most common cause is the Client Id: it must be only the unique code after
http://www.okta.com/, not the full issuer string. After that, check the Name ID format isEmailAddress. - Sign-in worked and then stopped. Okta signing certificates expire. Download the current certificate and re-upload it in the WestFax SSO panel.
Still stuck? Call us at 303-299-9329, contact our team, or reach out to your account manager.